
Open Kali Linux for the first time and you'll see hundreds of tools. Most beginners freeze here, or pick tools at random. Real testers don't. They follow a fixed order, and each phase tells you which tools make sense right now.
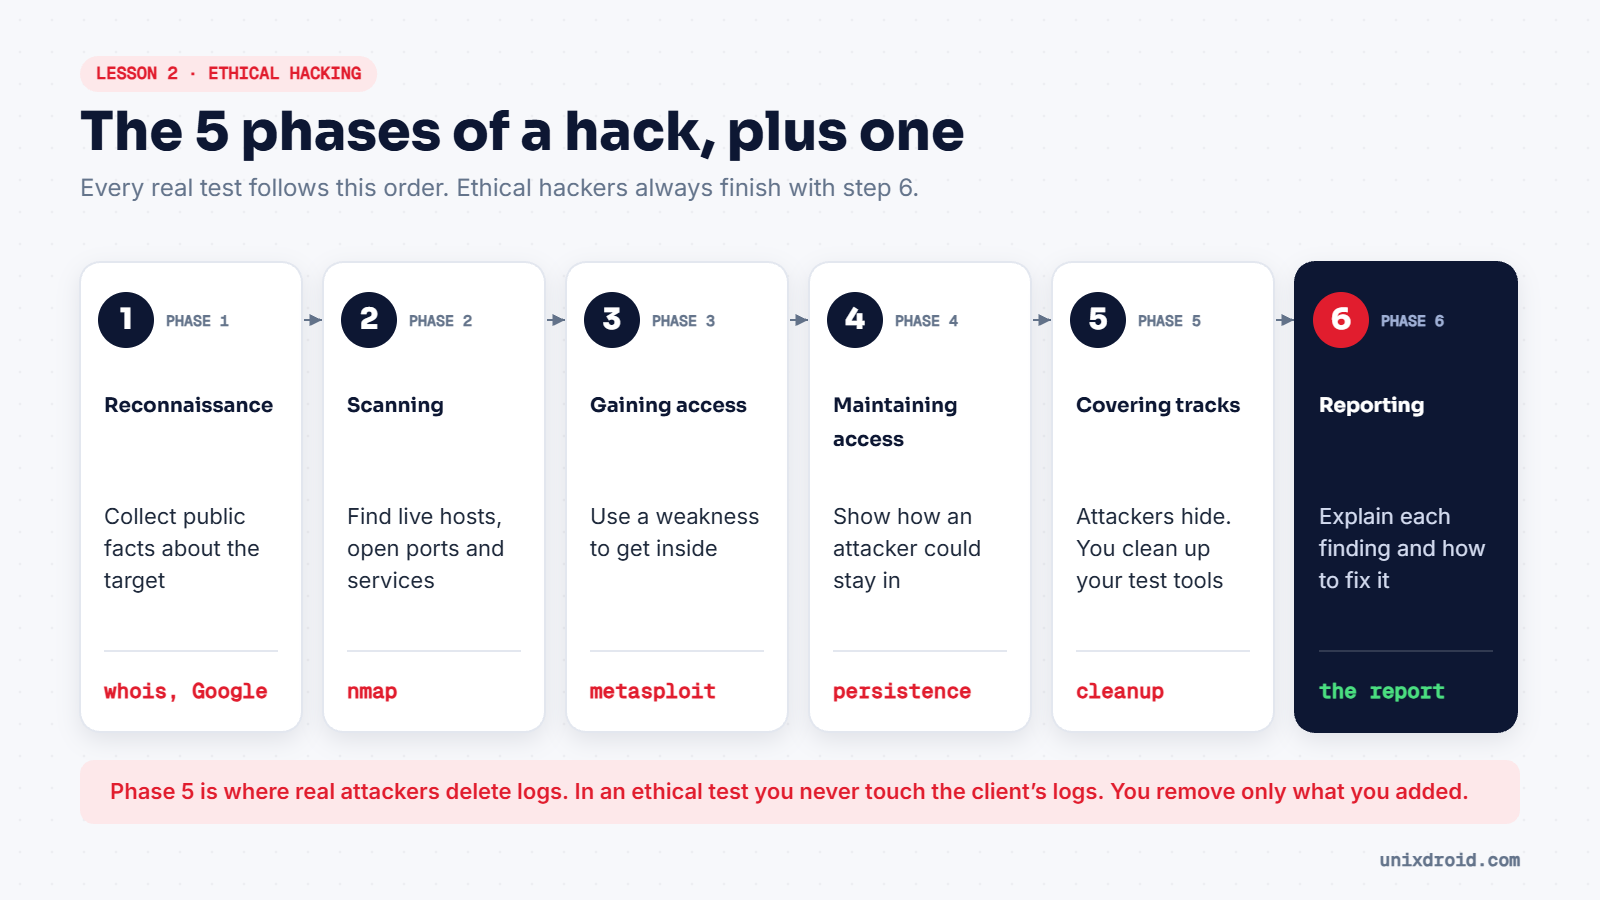
Phase 1: Reconnaissance
Collect as much information as you can about the target before you touch it: domain names, IP ranges, employee names, email formats, and the technologies their website uses. Good recon makes every later phase faster.
Example tools: whois, dig, Google search operators, theHarvester.
Phase 2: Scanning
Now you look at the target directly. Which machines are online? Which ports are open? What software, and which version, runs on each one?
Example tools: nmap, masscan, nikto for web servers.
Phase 3: Gaining access
This is the part films love. You use a weakness you found, such as an old software version, a weak password or a badly written web form, to get inside.
Example tools: Metasploit, Burp Suite, Hydra.
Phase 4: Maintaining access
A real attacker wants to come back later, so they set up a way to stay in, like a hidden user account or a backdoor. In an ethical test you show this is possible, within the rules you agreed, so the company understands how far a break-in could go.
Phase 5: Covering tracks
Criminals delete logs and hide files so nobody notices them. Ethical hackers do the opposite. You never delete the client's logs. You remove only the files, accounts and tools you added during the test, and you write down that you removed them.
Phase 6: Reporting
This is the phase that turns hacking into a profession. A good report explains:
- what you found, ranked by risk: critical, high, medium or low,
- how you found it, step by step, so their team can repeat it,
- how to fix it, in plain language a manager can follow.
A test without a clear report is worth very little to the client. Don't be surprised if writing it takes as long as the hacking did.
The phases aren't always a straight line. If scanning shows something new, you go back to recon. That's normal, and good testers do it all the time.
Where you'll learn each phase
| Phase | In this path |
|---|---|
| Reconnaissance | Lesson 4 |
| Scanning | Lesson 5 |
| Gaining access and beyond | Coming next |
Before any of that, you need a safe place to practise. That's the next lesson.