
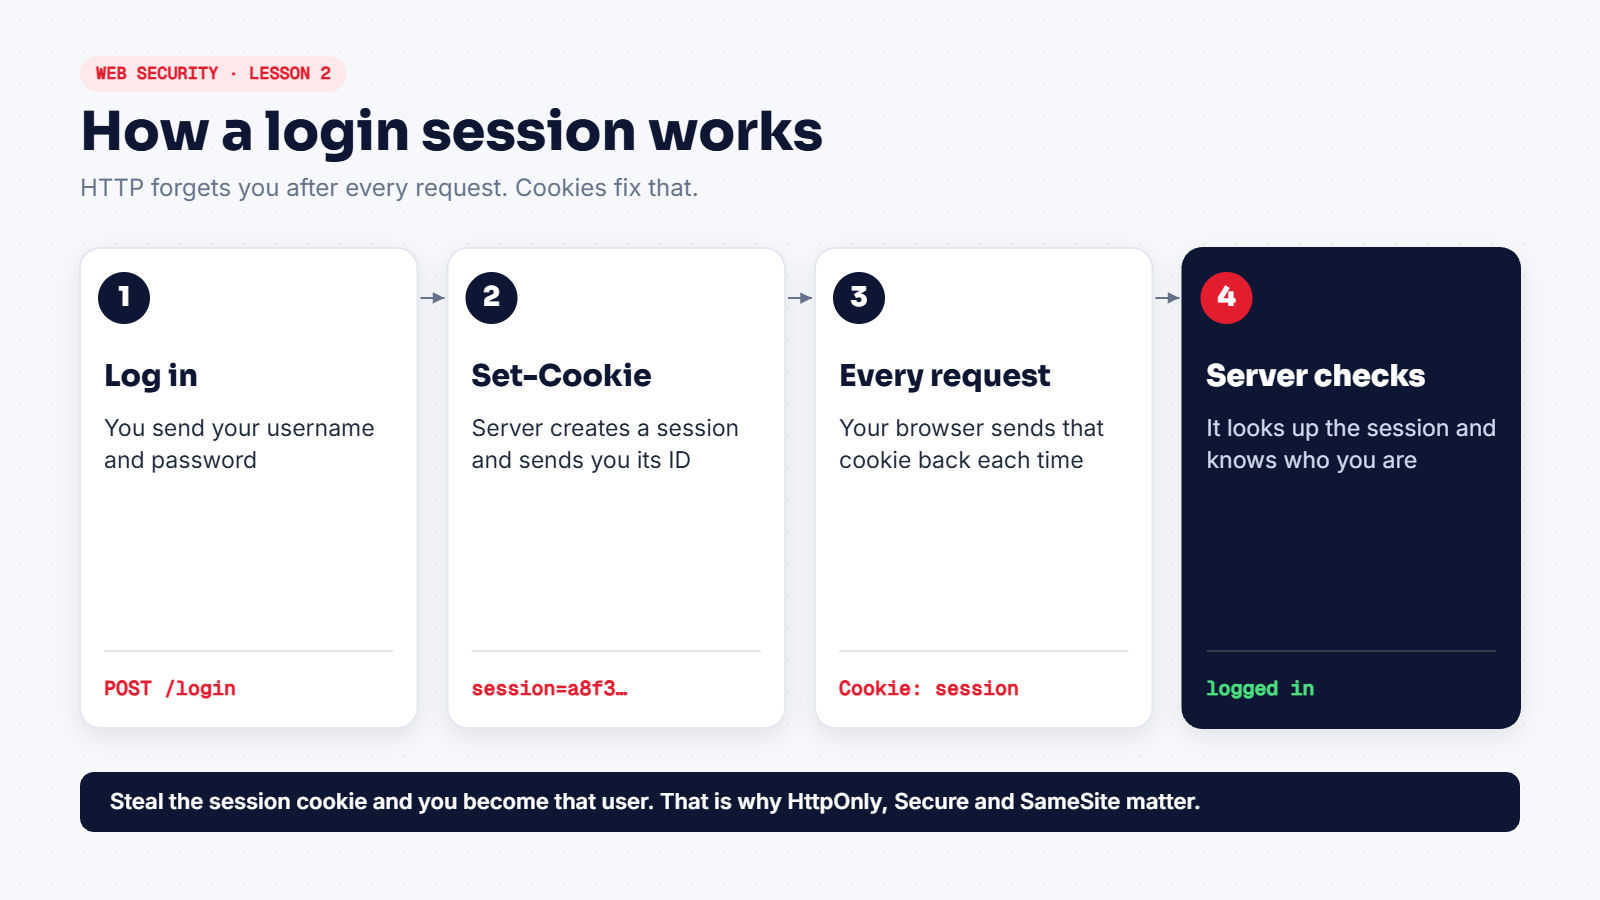
HTTP has no memory. Each request arrives on its own, with no idea that you logged in a second ago. Websites fix this with sessions, and sessions are carried by cookies.
See your own cookies
In Chrome, press F12, open the Application tab, then Cookies in the left panel. In Firefox it's the Storage tab. Log in to any site and you'll see a cookie with a long random value. That value is your session ID.
The security flags
| Flag | What it does |
|---|---|
HttpOnly | JavaScript can't read the cookie, so XSS can't steal it easily |
Secure | Only sent over HTTPS, never plain HTTP |
SameSite=Lax or Strict | Not sent on most requests from other websites, which helps against CSRF |
Expires / Max-Age | When the cookie dies |
A session cookie without HttpOnly and Secure is one of the most common findings in web tests.
How sessions get attacked
- Session hijacking: the attacker steals the cookie, often through XSS or an unencrypted connection, and pastes it into their own browser. No password needed.
- Session fixation: the attacker makes the victim use a session ID the attacker already knows, then waits for them to log in.
- Never-ending sessions: sessions that don't expire give stolen cookies a long life.
What good apps do
- Create a new session ID right after login, which kills fixation.
- Destroy the session on the server when you log out, not just in the browser.
- Expire idle sessions after a reasonable time.
- Set
HttpOnly,SecureandSameSiteon every session cookie.
When a site has a "log out of all devices" button, it is deleting every session it has stored for you on the server.